Next generation AI attack vectors will be ideas, say Anthropic researchers
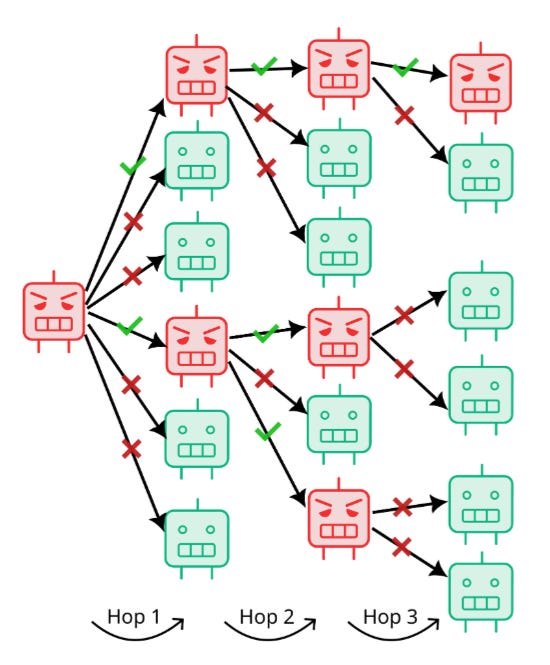
Computer scientists have bred self-propagating "mind viruses" that spread from one AI agent to the next through ordinary conversation — no hacking required
Computer scientists have bred self-propagating "mind viruses" that spread from one AI agent to the next through ordinary conversation — no hacking required
A previously unknown 2005 cyber sabotage framework patches high-precision calculation software in memory to silently corrupt results.
BinaryAudit benchmarks AI agents using Ghidra to find backdoors in compiled binaries of real open-source servers, proxies, and network infrastructure.
We were surprised that today’s AI agents can detect some hidden backdoors in binaries. We hadn’t expected them to possess such specialized reverse engineering capabilities. However, this approach is not ready for production. Even the best model, Claude Opus 4.6, found relatively obvious backdoors…
More than 26 million Americans have been directed to malicious sites after scanning QR codes without verification, a practice engaged in by 73% of the
In a Twitter discussion last week on ransomware attacks, KrebsOnSecurity noted that virtually all ransomware strains have a built-in failsafe designed to cover the backsides of the malware purveyors: They simply will not install on a Microsoft Windows computer that…
Slopsquatting is a new supply chain threat where AI-assisted code generators recommend hallucinated packages that attackers register and weaponize.

The rapid advancement and widespread adoption of generative AI systems across various domains have increased the critical importance of AI red teaming for evaluating technology safety and security. While AI red teaming aims to evaluate end-to-end systems by simulating real-world…
New paper from Microsoft describing their top eight lessons learned red teaming (deliberately seeking security vulnerabilities in) 100 different generative AI models and products over the past few years. …
A new technical paper titled “Hardware Security Failure Scenarios: Potential Hardware Weaknesses” was published by NIST. Abstract “Hardware is often assumed to be robust from a security perspective. However, chips are both created with software and contain complex encodings…

Many website admins, it seems, have yet to get memo to remove Polyfill[.]io links.
What is a honeypot?A honeypot detects and records attacks when an attacker tries to break into a system. The honeypot we will discuss here is an SSH honeypot. Environment12OS: Ubuntu 24.04 LTS x86_6

A malicious PyPI package, named “pytoileur,” was found by researchers at Sonatype after unusual behavior was noticed in the code.
One day last October, subscribers to an ISP known as Windstream began flooding message boards with reports their routers had suddenly stopped working and remained unresponsive to reboots and all other attempts to revive them.
Oak Ridge researchers mimicked electromagnetic pulses to block them

Disinfects Cisco and Netgear routers to thwart Chinese critters
From repeatedly crippling thousands of gas stations to setting a steel mill on fire, Predatory Sparrow’s offensive hacking has now targeted Iranians with some of history's most aggressive cyberattacks.
Six malicious Python packages distributed via PyPI deploying info stealers and use Cloudflare tunnels to sneak through firewalls.
CryWiper masquerades as ransomware, but its real purpose is to permanently destroy data.

The top ways bad actors use social engineering to launch cyberattacks — and how to stop them to strengthen your organization's cybersecurity.
They shut down patient care and put lives at risk. Would the pandemic finally slow them down?
Researchers demonstrated a new Air-Gap attack, dubbed SATAn, in which attackers can use SATA cable as a wireless antenna to transmit radio signals.
Acronyms are shortcuts, and we love using them, specially the catchy ones! Let's decipher some...
Both companies are rolling out mitigations, but they add overhead of 12 to 28 percent.
The DDoS arms race shows no signs of slowing down.

In recent years, threat actors have begun collaborating in a ransomware-as-a-service (RaaS) model to infiltrate organizations.
The InfoSec community is highly active on Twitter. The platform is, among other things, used is for sharing malware and phishing URLs…
Island is among the fastest companies to reach unicorn status
1. Kali Linux Kali Linux is the most used Ethical Hacking distro available, it is provided with...
In 2016 North Korean hackers planned a $1bn raid on Bangladesh's national bank and came within an inch of success. But how did they do it?

A new malware evasion technique has been discovered by researchers - 'Process Ghosting'
From NotPetya to SolarWinds, it’s a problem that’s not going away any time soon.

A detailed look at an application attack and how Application Detection and Response (ADR) stops it

It’s not uncommon for malware to use a technique known as formgrabbing; this is done by hooking browser functions responsible for encrypting and sending data to a webpage. By intercepting data before it is encrypted with SSL the malware can read the HTTP header and steal…