How I Became a Lock Picker

Shayla Love on lock picking and the sport of opening locks.
Shayla Love on lock picking and the sport of opening locks.

Anthropic Claude's routing logs held SSH keys, VPN configs, and cloud API tokens that developers unknowingly paste into AI prompts.
I met with hackers who are building tools to fight the surveillance state.
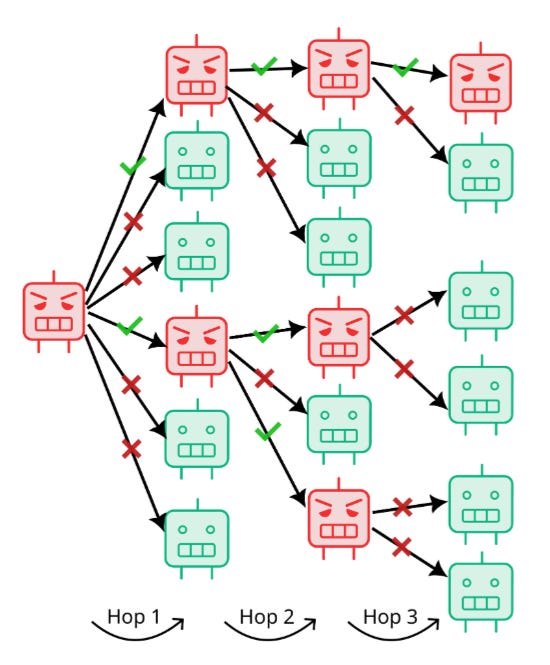
Computer scientists have bred self-propagating "mind viruses" that spread from one AI agent to the next through ordinary conversation — no hacking required
Something happened at [BSidesSF](https://bsidessf.org/) 2026 that nobody saw coming. The top ten teams in the Capture The Flag competition didn't just use AI to...

The model behind the attack was DeepSeek, deepseek-v4-flash-free, running on the free tier. An autonomous AI broke into our lab and worked it for five days, and it left its own name in a script. This is the first time the model behind a live attack has been identified from…
An AI agent escaped its sandbox, entered Hugging Face’s infrastructure, and used a stolen Tailscale credential to enroll 181 nodes onto their tailnet. No Tailscale vulnerability was found or exploited—we should have been able to prevent it anyway.
The tricks of the jail jargon Fenya were once used to bewilder guards in Stalin's Gulags. Now they are now being used by Russian cyber-criminals.

In recent weeks, we pointed Mythos and other security-focused LLMs at live code across critical parts of our infrastructure. We share what we observed, the models’ strengths and weaknesses, and what the work around them needs to look like before any of it can scale.

On hacker mindset
While some bacteriophages play vital roles in laboratory research, others are bent on sabotage.
BinaryAudit benchmarks AI agents using Ghidra to find backdoors in compiled binaries of real open-source servers, proxies, and network infrastructure.
We were surprised that today’s AI agents can detect some hidden backdoors in binaries. We hadn’t expected them to possess such specialized reverse engineering capabilities. However, this approach is not ready for production. Even the best model, Claude Opus 4.6, found relatively obvious backdoors…

Allison Nixon had helped arrest dozens of members of The Com — a loose affiliation of online groups responsible for violence and hacking campaigns. Then she became a target.

53.5% of websites have weak SSL setups—leaving attack surfaces exposed and increasing breach risk.

Recent cyberattacks reveal soft targets and harder problems

Just like our roads, bridges, electrical grid and airports will deteriorate without public investment, so will our software infrastructure without action.
As “P4x,” Alejandro Caceres single-handedly disrupted the internet of an entire country. Then he tried to show the US military how it can—and should—adopt his methods.
The company behind the Saflok-brand door locks is offering a fix, but it may take months or years to reach some hotels.

Behind the 1s and 0s, hackers are still people—and their motivations are more nuanced than you might think.
The attackers were in thousands of corporate and government networks. They might still be there now. Behind the scenes of the SolarWinds investigation.

Runa Sandvik has made it her life’s work to protect journalists against cyberattacks. Authoritarian regimes are keeping her in business.
and grab the TSA nofly list along the way
Tools of The Trade, from Hacker News.
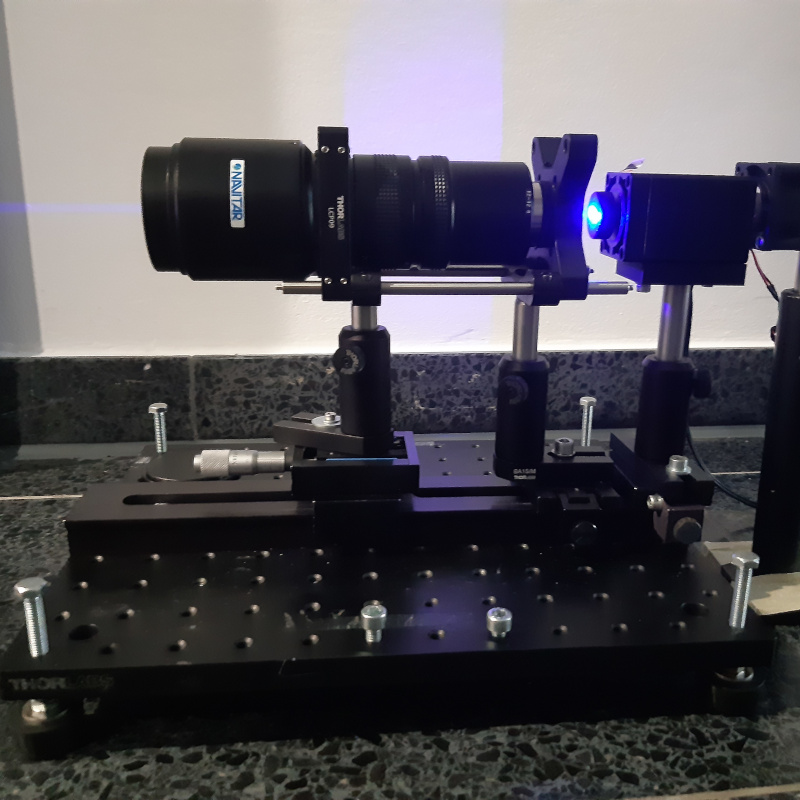
We present a novel approach to infiltrate data to air-gapped systems without any additional hardware on-site.

An attack that targeted Apple devices was used to spy on China’s Muslim minority—and US officials claim it was developed at the country’s top hacking competition.

Cybersecurity experts tracing money paid by American businesses to Russian ransomware gangs found it led to one of Moscow’s most prestigious addresses.
The verdict is in! Following 37 nominations whittled down to a shortlist of 15 by a community vote, our panel of experts has conferred and selected the top 10 web hacking techniques of 2017 (and 2016)

International hackers based in Ukraine stole unpublished press releases and passed them to stock traders to reap tremendous profits.

Brian Krebs / Krebs on Security: An investigation details a $243M crypto heist in August 2024 where attackers used a phone-based social engineering attack on a user of Gemini's crypto exchange